Permissions set for users in Active Directory Groups are not seen
Article ID: 144855
Updated On:
Products
CA Client Automation - IT Client Manager
CA Client Automation
Issue/Introduction
Active Directory groups are added as security profile with a set of class permissions. But user belonging to this AD group has not the class permissions set.
For example when trying to open DSM GUI, the login dialog box appears even if we are logged with a user belonging to a AD group which has full rights in ITCM.
There is same problem with RC permissions, User has no permission to take control of machines even if he belongs to a AD group with RC permissions
Environment
All Client Automation versions
Cause
This problem occurs if there are 2 or more AD Domains and AD group are Local Domain group.
The scope of AD Local Group is only the AD Domain where it is created and it is not seen outside the AD Domain
Resolution
In Active Directory change the "Group Scope" of the group from "Domain Local" to "Global" :
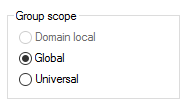
This group will be seen outside its AD Domain.
This group will be seen outside its AD Domain.
Feedback
Yes
No
Powered by
